| NGFW |
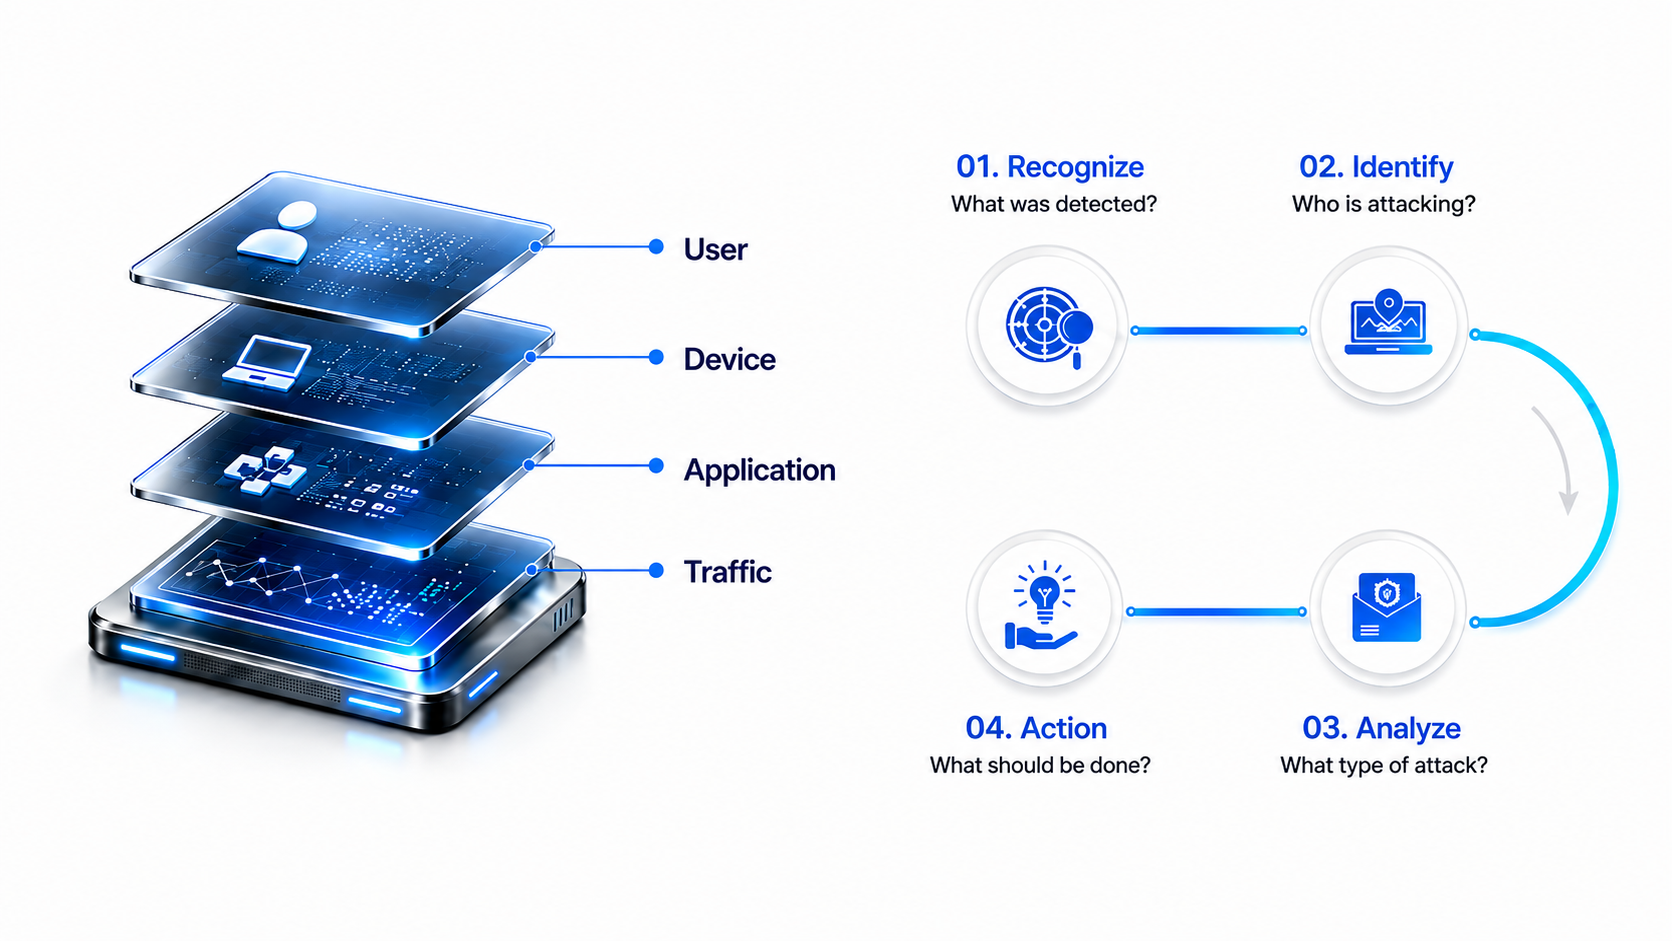
- Comprehensive defense from L3/L4 network layers to L7 application-layer attacks (behavior-based web attacks, DRDoS, etc.)
- Integrated policy control based on users, devices, and applications (including SaaS)
- Various user authentication and identification (Captive Portal, AD SSO integration)
- Support for user-defined application patterns (Custom Pattern)
|
| Anti DDoS Network |
- Granular profile-based threshold settings per protected domain
- Customized QoS based on applications, users, and web categories
- Real-time attacker detection and blocking, packet dump, and exception host management
|
| Anti-Virus & Anti-SPAM |
- Real-time mail protocol and attachment malware inspection/removal with high-performance Anti-Virus engine
- Precise spam filtering via real-time blacklist (RBL), spam score, and PCRE keyword matching
|
| Web Filter |
- Powerful category-based web filtering with harmful-site DB and global URL reputation DB
- Blocking based on domain, IP address, PCRE patterns, and extended URL inspection (query string)
- In-depth web security analytics and URL match simulation (custom warning pages supported)
|
| User Authentication |
- Integration with diverse external auth servers and DBMS (AD, LDAP, RADIUS, etc.)
- Flexible Captive Portal authentication policies supporting both IPv4/IPv6
- OTP-based MFA profile configuration and detailed authentication log monitoring
|
| Firewall |
- IPv4/IPv6 firewall policies and blacklist policies (with exceptions)
- Precise access control based on domain (URL objects) and country (GeoIP)
- L2 layer defense (MAC filter) and logical security policy grouping
- Flexible security policy management based on time and schedules
- Various network address translations (S-NAT, D-NAT, Double NAT)
- LSNAT (SNAT/DNAT pool) load balancing for large-scale traffic processing
- Policy simulation for validity and safety verification
- Policy operation optimization via unused object/policy and duplicate policy search
- Real-time monitoring of policy hit counts and session matching status
- One-click linkage between policy configuration and log analysis
- Import/Export for large-scale security policy management
|
| IPsec VPN |
- Strong IKEv1/IKEv2 and PKI-based authentication with diverse standard encryption and integrity algorithms
- High-performance data plane processing via proprietary kernel module (HW acceleration) and multi-tunneling (GRE, L2TP, etc.)
- Non-stop VPN failover and load balancing via DPD, DR connectivity, and line failure detection
- Full support for diverse network environments (L3, Bridge, Bonding, etc.) and intuitive tunnel monitoring
|
| SSL VPN |
- Strong access control with ONE-PASS URL (QR code) authentication and MFA (ID/PWD, certificate, OTP)
- Full IPv6 support and Full/Split tunneling for traffic optimization
- Support for PC, mobile, embedded devices, and automatic client updates
- Granular leased IP assignment and customized security access control per user group
|
| SD-WAN |
- Intelligent automatic traffic path control based on applications and policies (IPv4/IPv6)
- Profile-based simplified SD-WAN environment configuration for maximum manageability
|
| Virtual Domain |
- Multiple Virtual Domains (namespace-based multi-tenant architecture)
- Independent security policies and system resource allocation per VD (virtual domain)
|
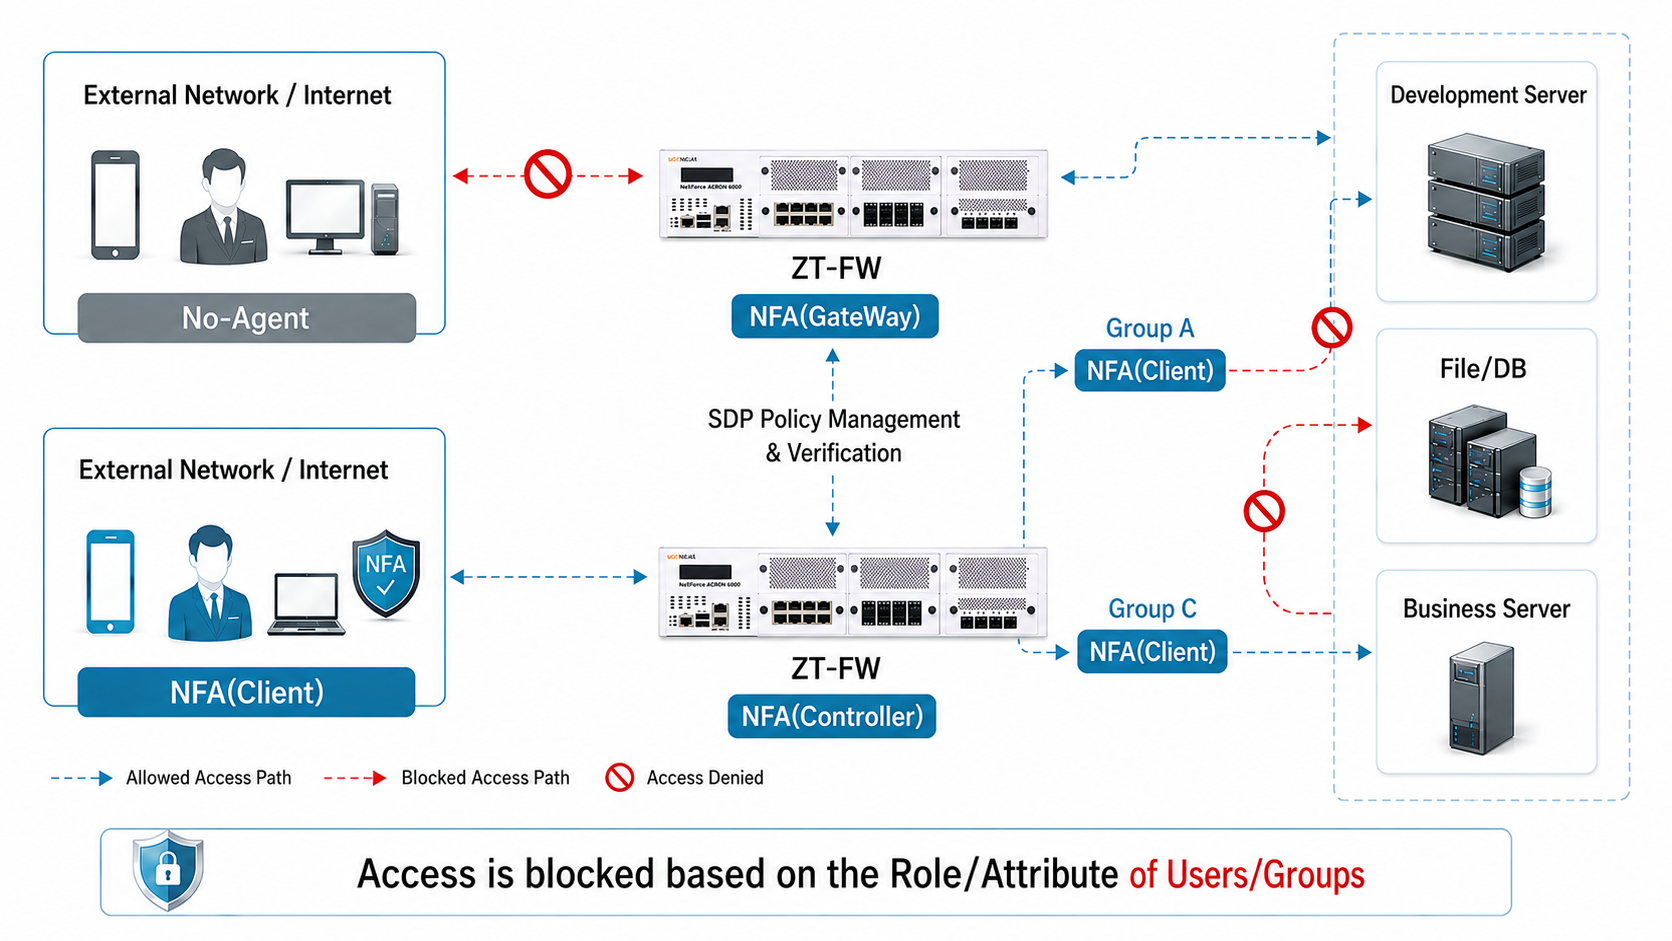
| ZTNA / SDP |
- Integrated configuration of controller, gateway, and agents (Windows, Android)
- Dynamic least-privilege access control based on user identity and endpoint integrity verification
- SPA-based infrastructure concealment (Stealth Mode) and dynamic encrypted secure channel formation
|
| N2SF |
- Complete internal logical network segmentation based on Zero Trust architecture
- Security zone configuration and differentiated access control based on data classification
- Traffic isolation and precise control (L7 inspection, content control) between security zones
- Real-time zone policy violation detection/alerts and compliance evidence reporting
|
| Quantum Security |
- VPN with global (NIST) and domestic (KpqC) standard post-quantum cryptography (PQC) algorithms
- Highest-level unpredictable cryptographic key generation via QRNG (Quantum Random Number Generator) integration
|
| Network |
- Various IPv4/IPv6 dynamic routing (OSPF, BGP, etc.) and multicast support
- Stable non-stop L2/L3 switching environment with LACP (Bonding), VLAN, STP, etc.
- Essential network services for flexible infrastructure: DHCP/DHCPv6, DNS, DDNS
- Granular network bandwidth quality assurance (QoS) based on IP, application, and interface
- Complete IPv6 transition support for heterogeneous networks: NAT64, NAT46, tunneling (6to4), etc.
|
| Device Control |
- Zero Trust access control based on user and endpoint identifiers (Device Identity)
- Endpoint integrity assurance through mandatory security compliance checks (antivirus/patch/encryption, etc.)
|
| HA |
- Non-stop session and configuration synchronization via Active-Active / Active-Standby and L4 Cluster
- Selective (granular) failover support per VIP/session sync group
|
| Monitoring |
- Comprehensive integrated monitoring dashboard (network, VPN, threats, user status, etc.)
- Real-time endpoint risk score evaluation and automatic blocking of unauthorized/threat endpoints
- DB-based large-scale log management and multi-layer threat analysis
- Threshold-based real-time alerts (email/SMS/popup) and customized reports
|
| DLP |
- Control of internal critical data exfiltration via precise file type and content analysis
- Precise pattern detection and blocking of sensitive personal information and core business keywords
|
| SSL Inspection |
- Decryption of latest encryption protocols (TLS 1.2/1.3, HTTP/2) and multi-traffic (HTTPS, SMTPS, etc.)
- Deep integrated inspection without blind spots via IPS, Web Filter, and Anti-Virus on decrypted traffic
- Capacity control (threshold settings) to prevent system overload and flexible decryption exceptions via SNI
- Multi-CA certificate management per profile and precise HTTP/2 path-level filtering
|
| Management |
- Multi-level administrator permission profiles and security authentication control (LDAP, OTP integration, etc.)
- System stability via integrity verification, firmware rollback (downgrade), backup/recovery
- Intuitive operational convenience: Setup Wizard, GUI packet capture, system batch diagnostics
- Flexible integration with external security solutions via Open API (REST)
|
| AI Security |
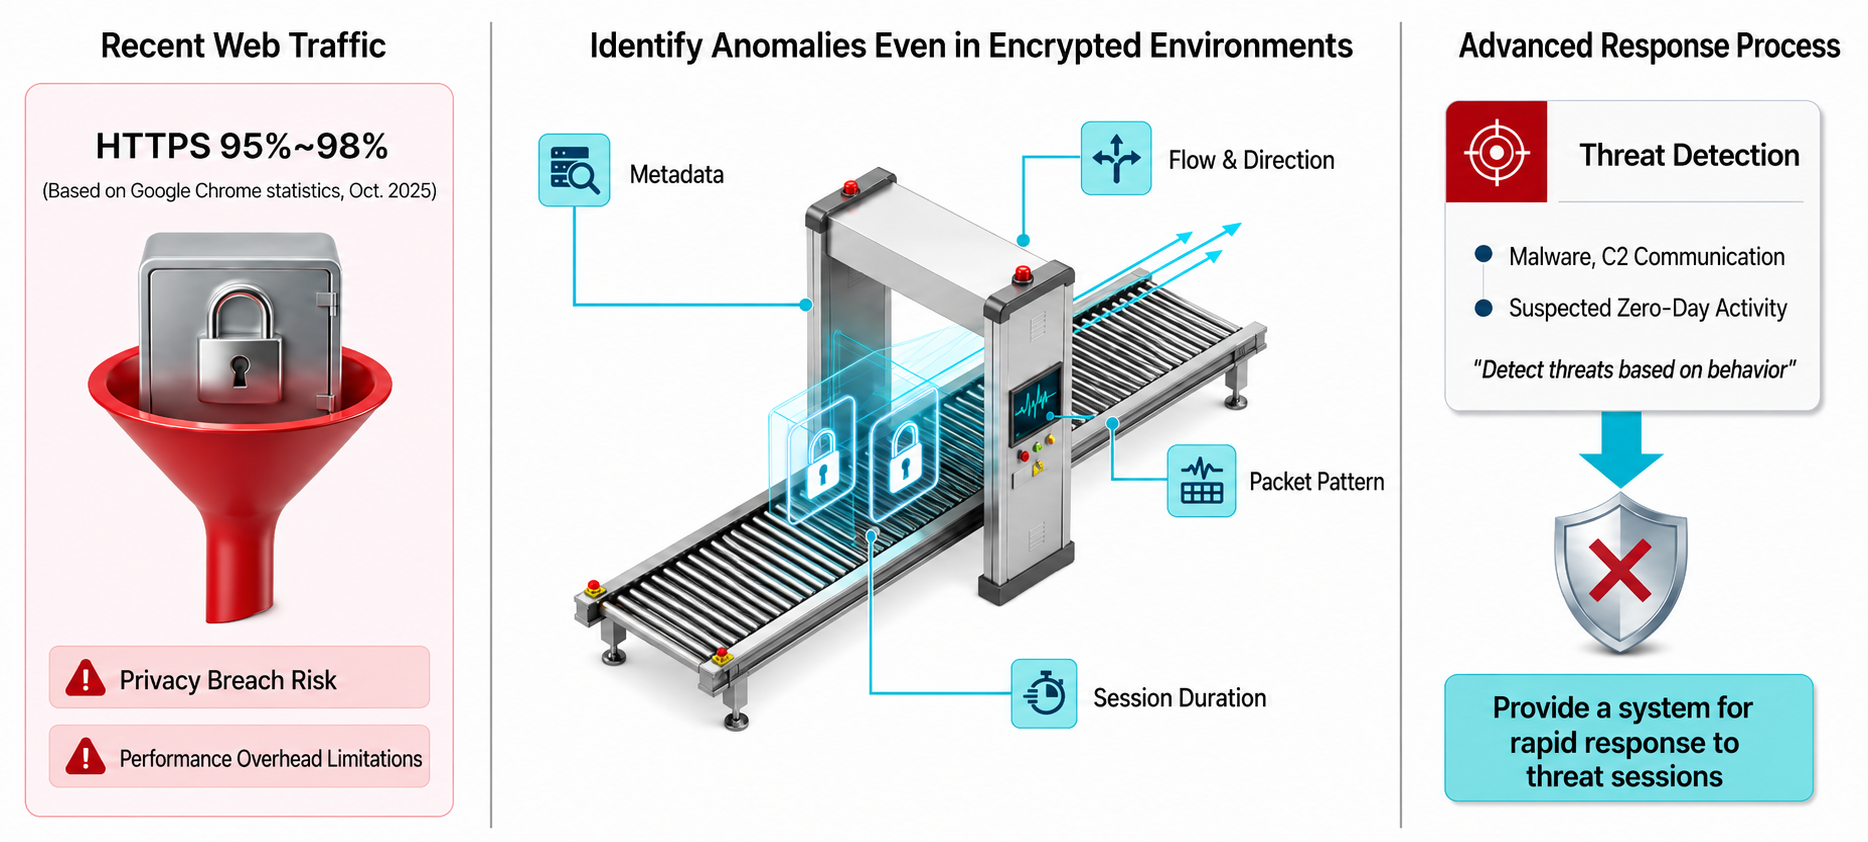
- AI security assistant supporting LLM-based natural language threat analysis and automatic anomaly selection
- Proactive blocking of zero-day and abnormal communication (C2) via AI engine-based encrypted traffic deep analysis
|
| IPS |
- Automated signature DB updates for latest threat response and multi-pattern detection engine
- Profile-based customized defense and user-defined signatures using PCRE (regular expressions)
|